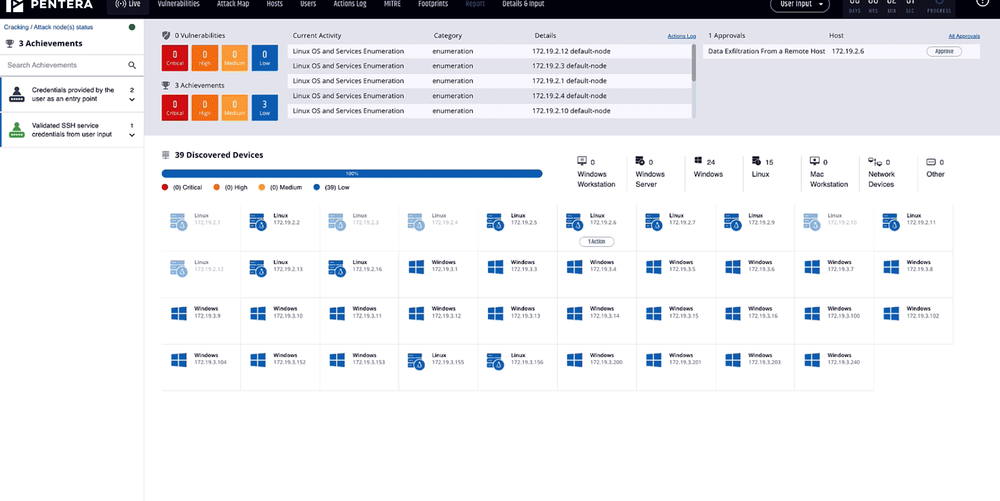
Penetration Testing
Validate Security. Prioritise Real Risk.
We provide you with the best security validation platform that continuously tests your defences against real-world attack techniques, giving you an always-on view of what is truly exploitable so your team remediates the risks that matter most.
Check out the featuresGet Expert Advice
Our Preferred Vendor

Continuous Validation for Real-World Security
Organisations face an ever-evolving threat landscape, making it challenging to ensure their security controls are truly effective against real-world attacks. Traditional penetration testing is often infrequent and resource-intensive, leaving significant gaps in understanding your actual exposure to risk and leading to inefficient allocation of remediation resources.
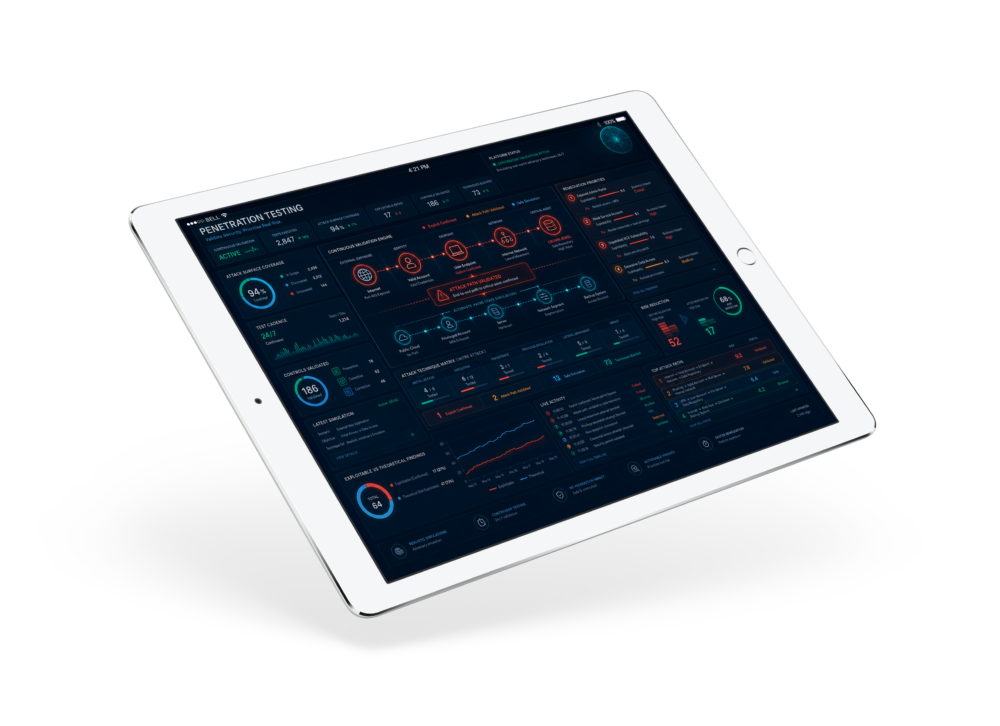
The solution we provide automates security validation and penetration testing, providing continuous, real-time insights into your organisation’s exploitable vulnerabilities. By emulating real-world attack techniques safely in production environments, we help your security team proactively identify and prioritise critical risks, enabling a data-driven approach to remediation that focuses resources on the most impactful security improvements.
Enhanced Attack Readiness
This solution provides continuous and systematic security control validation, keeping your organisation constantly updated on its security status and improving readiness against cyber threats, without waiting for the next scheduled assessment.
The platform delivers significant operational benefits by automating assessments and reducing the need for manual red team execution, freeing up valuable security team resources for higher-priority strategic work.
Optimised Security Operations
Data-Driven Risk Prioritisation
By proving what is exploitable in your specific environment, Sertalink helps your organisation prioritise real risks, ensuring that remediation efforts are focused on vulnerabilities that pose the greatest actual threat to the business.
Sertalink transforms penetration testing from a periodic event into a continuous program, giving your security team the evidence they need to make confident, risk-informed decisions about where to invest their remediation efforts.
Key Solution Features
Eliminate guesswork from your security programme and give your security team a strong foundation to validate defences faster and smarter. Pentera delivers the most comprehensive automated security validation capabilities for enterprises seeking continuous assurance.

Automated Penetration Testing
Run continuous, production-safe penetration tests that emulate real-world adversaries across your entire environment, without disrupting operations.

Attack Surface Mapping
Continuously discover and map your full attack surface, including shadow IT and unknown assets, to ensure nothing falls outside the scope of your security programme.

Exploitability Validation
Go beyond vulnerability scanning by proving which vulnerabilities are actually exploitable in your environment, eliminating false positives and alert fatigue.

Cloud Security Validation
Extend automated security validation to cloud environments, testing configurations, permissions, and workloads against real attack techniques.

Risk-Based Remediation Guidance
Receive prioritised, actionable remediation guidance ranked by actual business impact, enabling security teams to fix the most critical issues first.

Remediation Verification
Automatically re-test after remediation to confirm that fixes are effective, providing continuous proof of security improvement over time.
pentera spotlight
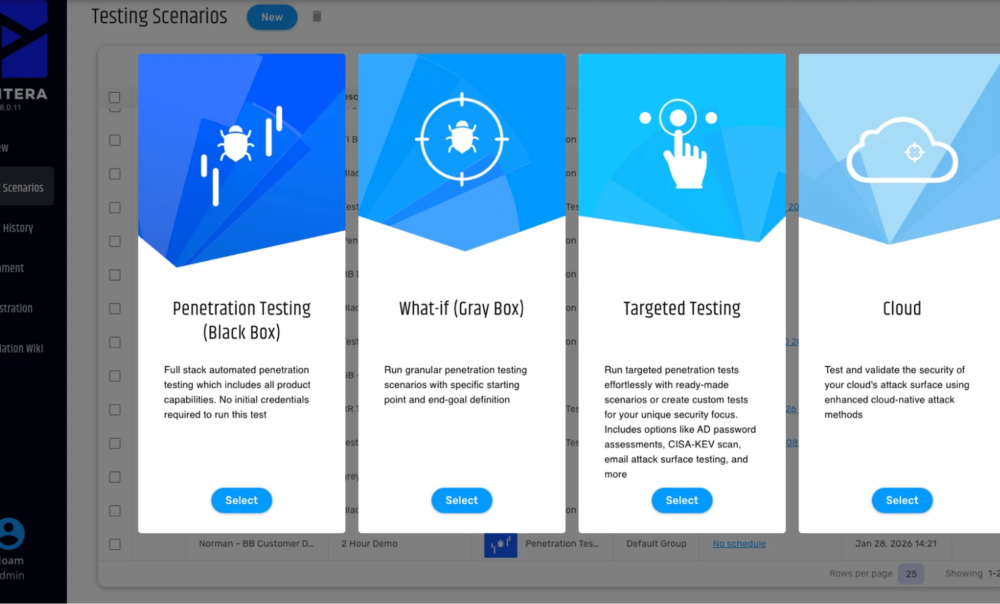
Pentera is built for security teams that need continuous, evidence-based assurance that their defences are working. It replaces periodic, resource-intensive manual testing with an always-on validation engine that delivers real-world attack emulation, exploitability proof, and prioritised remediation guidance at the pace of modern threats.
feature spotlight
Automated Attack Emulation
Pentera’s platform utilises algorithmic and AI-driven attacks to emulate real-world adversarial techniques safely in live production environments. This continuous security validation proves what is exploitable, prioritises risks based on actual business impact, and automates remediation verification giving security teams the evidence they need to act with confidence.
feature spotlight
Continuous Security Posture Management
Pentera provides an always-on view of security posture, tracking changes in the attack surface over time and alerting teams when new exploitable paths emerge. This continuous monitoring capability transforms security validation from a point-in-time exercise into an ongoing programme that keeps pace with the evolving threat landscape.