Extended Detection & Response
Unified Threat Detection & Response Across Every Layer
We deliver a fully integrated XDR platform, combining SIEM, EDR, NDR, UEBA, and SOAR, that correlates threats across your entire attack surface and responds at machine speed, so sophisticated attacks are stopped before they cause damage.
Check out the featuresGet Expert Advice
Trusted all around the globe


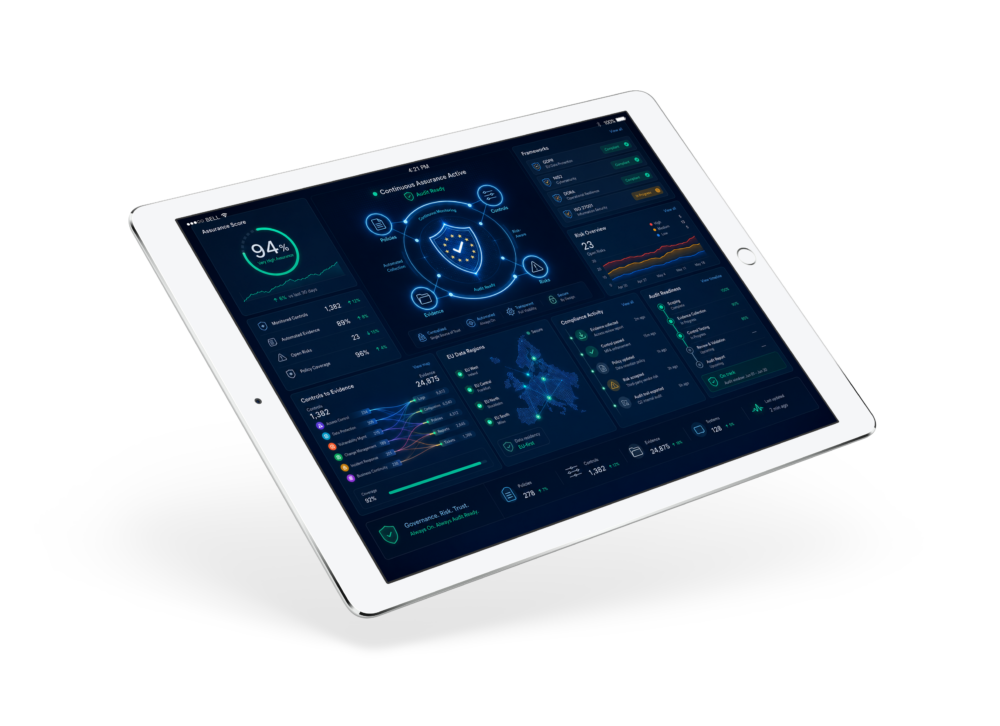
Breaking Down Security Silos Across the Full Kill Chain
Modern adversaries do not limit themselves to a single attack surface. They move laterally from endpoints to identities, pivot through the network, and escalate privileges into cloud environments, all within a single campaign. Traditional point products operating in isolation generate fragmented alerts, create blind spots, and overwhelm security teams with noise rather than actionable intelligence.
The XDR solutions we provide unify detection and response across endpoints, identities, network traffic, cloud workloads, and log data into a single correlated view. By ingesting and correlating telemetry from every layer simultaneously, XDR eliminates the gaps that attackers exploit and empowers your SOC to detect, investigate, and contain threats in minutes, not days.

Autonomous Threat Prevention
The AI-native endpoint and identity layer prevents, detects, and responds to threats at machine speed, stopping ransomware, malware, fileless attacks, and credential-based intrusions before they cause damage. Autonomous rollback capabilities restore affected systems instantly without manual intervention, dramatically reducing mean time to remediate.
The SIEM and log correlation layer centralises telemetry from every source across your hybrid environment, Active Directory, cloud platforms, firewalls, endpoints, and applications, into a single, searchable data lake. AI-driven UEBA establishes behavioural baselines and surfaces anomalies that signature-based tools routinely miss, including insider threats and slow-burn APT campaigns.
Unified Visibility & Behavioural Analytics
Accelerated SOC Efficiency
The combined XDR platform reduces alert noise, automatically correlates related events into high-fidelity incidents, and orchestrates response actions through pre-built SOAR playbooks. Your analysts focus on strategic decisions rather than manual triage of thousands of low-confidence alerts, enabling a leaner, faster, and more effective security operation.
Feature Highlights
Eliminate security silos and give your team a unified foundation to detect and respond to threats faster and smarter. These platforms deliver complementary, AI-native protection across every layer of the modern hybrid attack surface.

AI-Native Endpoint Protection
(SentinelOne, Crowdstrike)
AI-powered prevention, detection, and response for endpoints, IoT, and cloud workloads, stopping known and unknown threats autonomously with 1-click rollback.

Identity Threat Detection & Response
(SentinelOne, Crowdstrike)
Detect and disrupt identity-based attacks including credential theft, pass-the-hash, and privilege escalation, safeguarding user accounts and preventing lateral movement.

SIEM & Log Management
(ManageEngine)
Centralised log ingestion, correlation, and long-term retention across 750+ sources. Compliance-ready reporting for GDPR, NIS2, PCI DSS, and ISO 27001

Multi-Cloud Security Coverage
(SentinelOne, Crowdstrike, ManageEngine)
Protection extends to multi-cloud infrastructures, ensuring consistent security policies and threat detection across AWS, Azure, GCP, and SaaS applications.

Behavioural AI & UEBA
(SentinelOne, Crowdstrike, ManageEngine)
Advanced AI and machine learning identify sophisticated attack patterns and zero-day threats by understanding normal behaviour and spotting meaningful deviations, including insider threats.

Automated investigaiton & SOAR
(SentinelOne, Crowdstrike, ManageEngine)
Automated triage, correlation, and prioritisation of threats facilitates rapid investigation and orchestrated response, reducing mean time to respond across all attack vectors.
VENDOR SPOTLIGHT
The XDR solutions we provide are built for security teams that need comprehensive, AI-driven threat detection and response across the full attack surface. Together they replace siloed security tools with a unified, intelligent defence platform that delivers autonomous protection, behavioural detection, and accelerated response, from the endpoint to the cloud and across every log source.
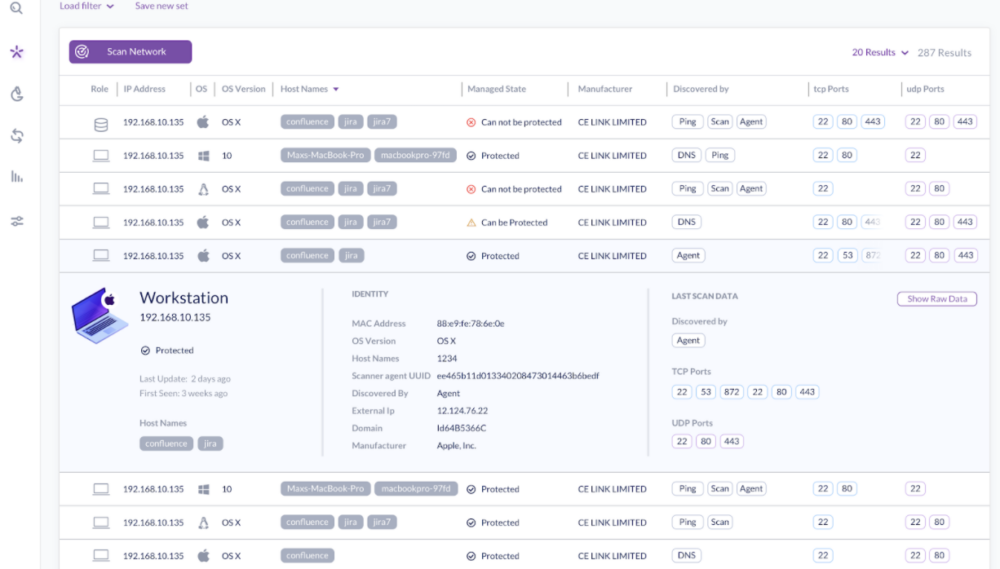
sentinelone spotlight
Singularity Platform
The Singularity Platform is SentinelOne’s AI-native XDR solution, unifying endpoint, identity, cloud, and network security into a single autonomous defence layer. It provides machine-speed prevention against ransomware, malware, and fileless attacks with 1-click rollback capabilities.
crowdstrike spotlight
Falcon XDR
The Falcon platform deploys an AI-native sensor across every endpoint to detect and stop breaches in real time, before they execute. With 100% detection scores in MITRE ATT&CK Evaluations and Charlotte AI delivering agentic triage at 98% accuracy, Falcon XDR delivers unmatched enterprise-grade protection.
manageengine spotlight
Log360
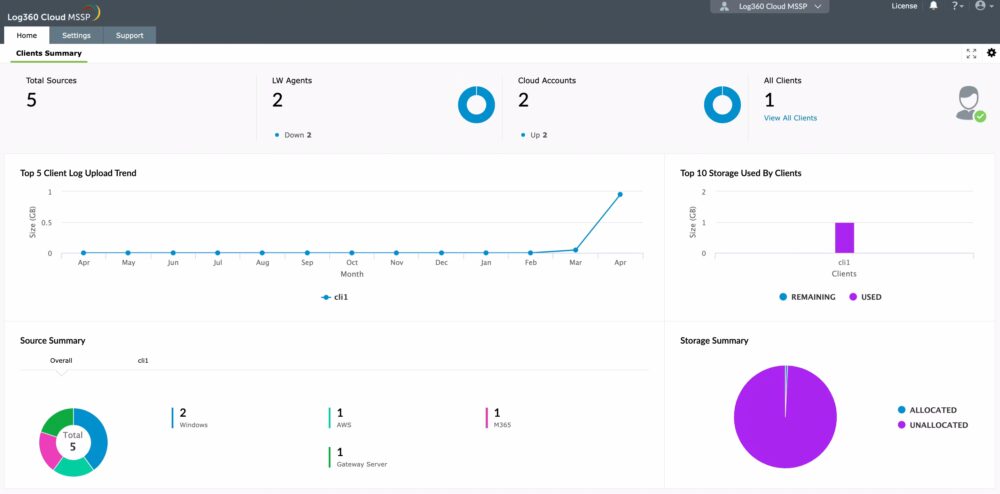
Log360 is the SIEM backbone of the XDR architecture, centralising logs from 750+ sources including Active Directory, cloud platforms, firewalls, and endpoints into a single correlated data lake. As Sertalink’s exclusive ManageEngine partner, we deploy and manage Log360 as the compliance and visibility layer of every XDR engagement.
